Cloud foundations
GCP architecture, IAM, private networking, managed runtimes, and cost-aware platform decisions.
Cloud Platform Engineering · United States
Cloud Platform Engineer
Building reliable, automated, and secure cloud infrastructure for teams that need clarity in production.
I work across GCP, AWS, Terraform, Kubernetes, DevSecOps, SRE, and observability, connecting architecture decisions to reliable delivery and day-two operations.
Featured engineering work
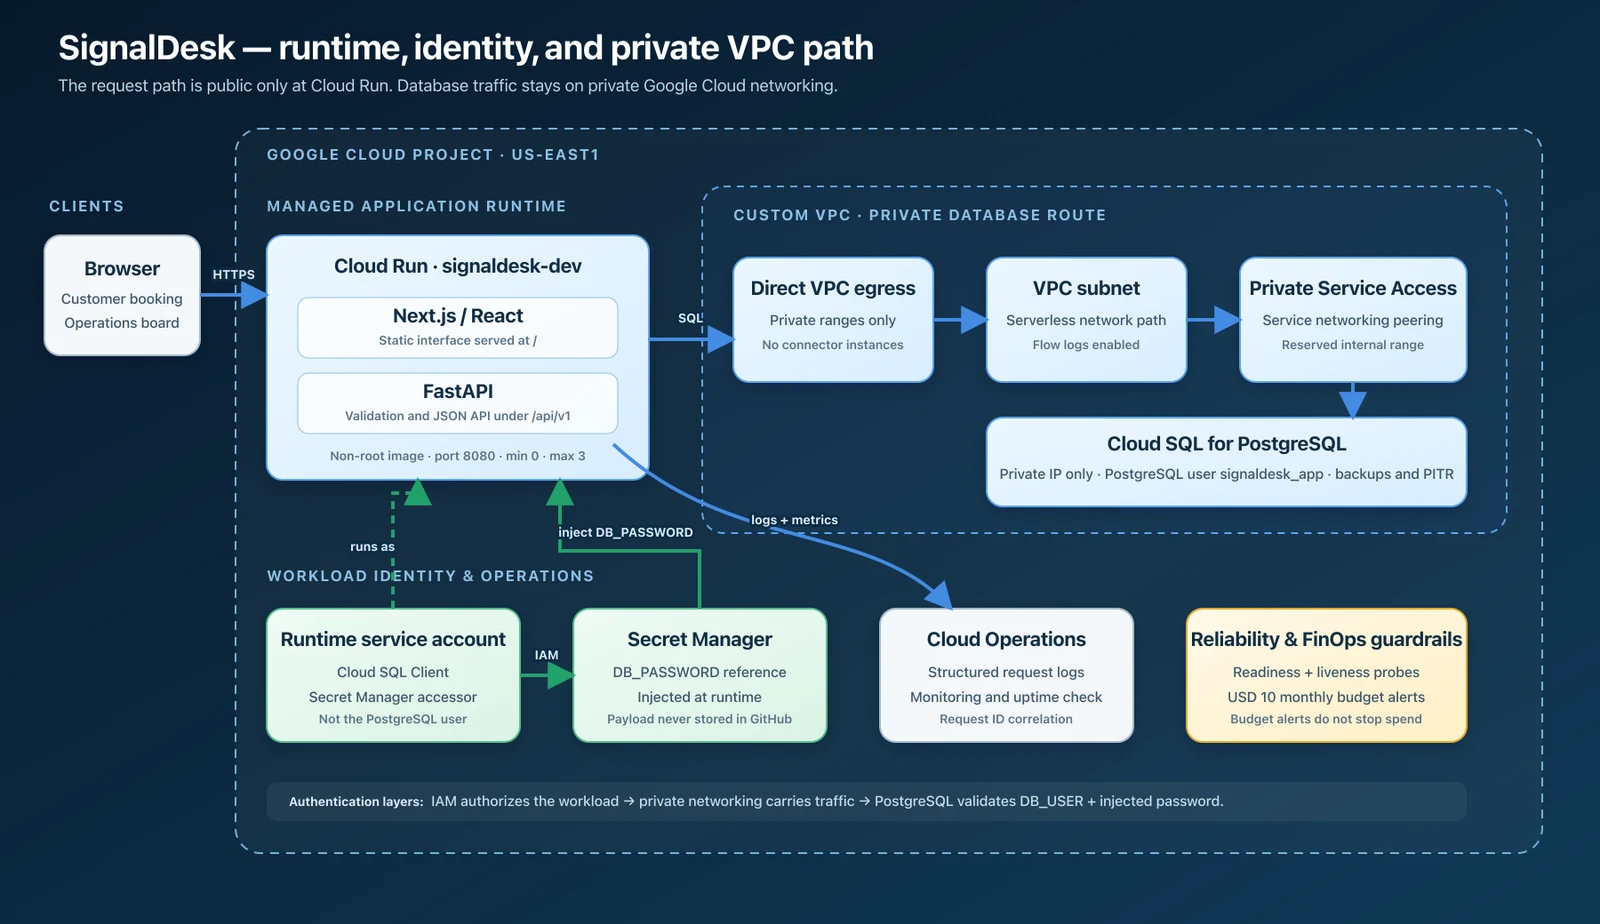
A production-oriented GCP implementation documented from architecture and delivery through observability and cost control.
Engineering brief
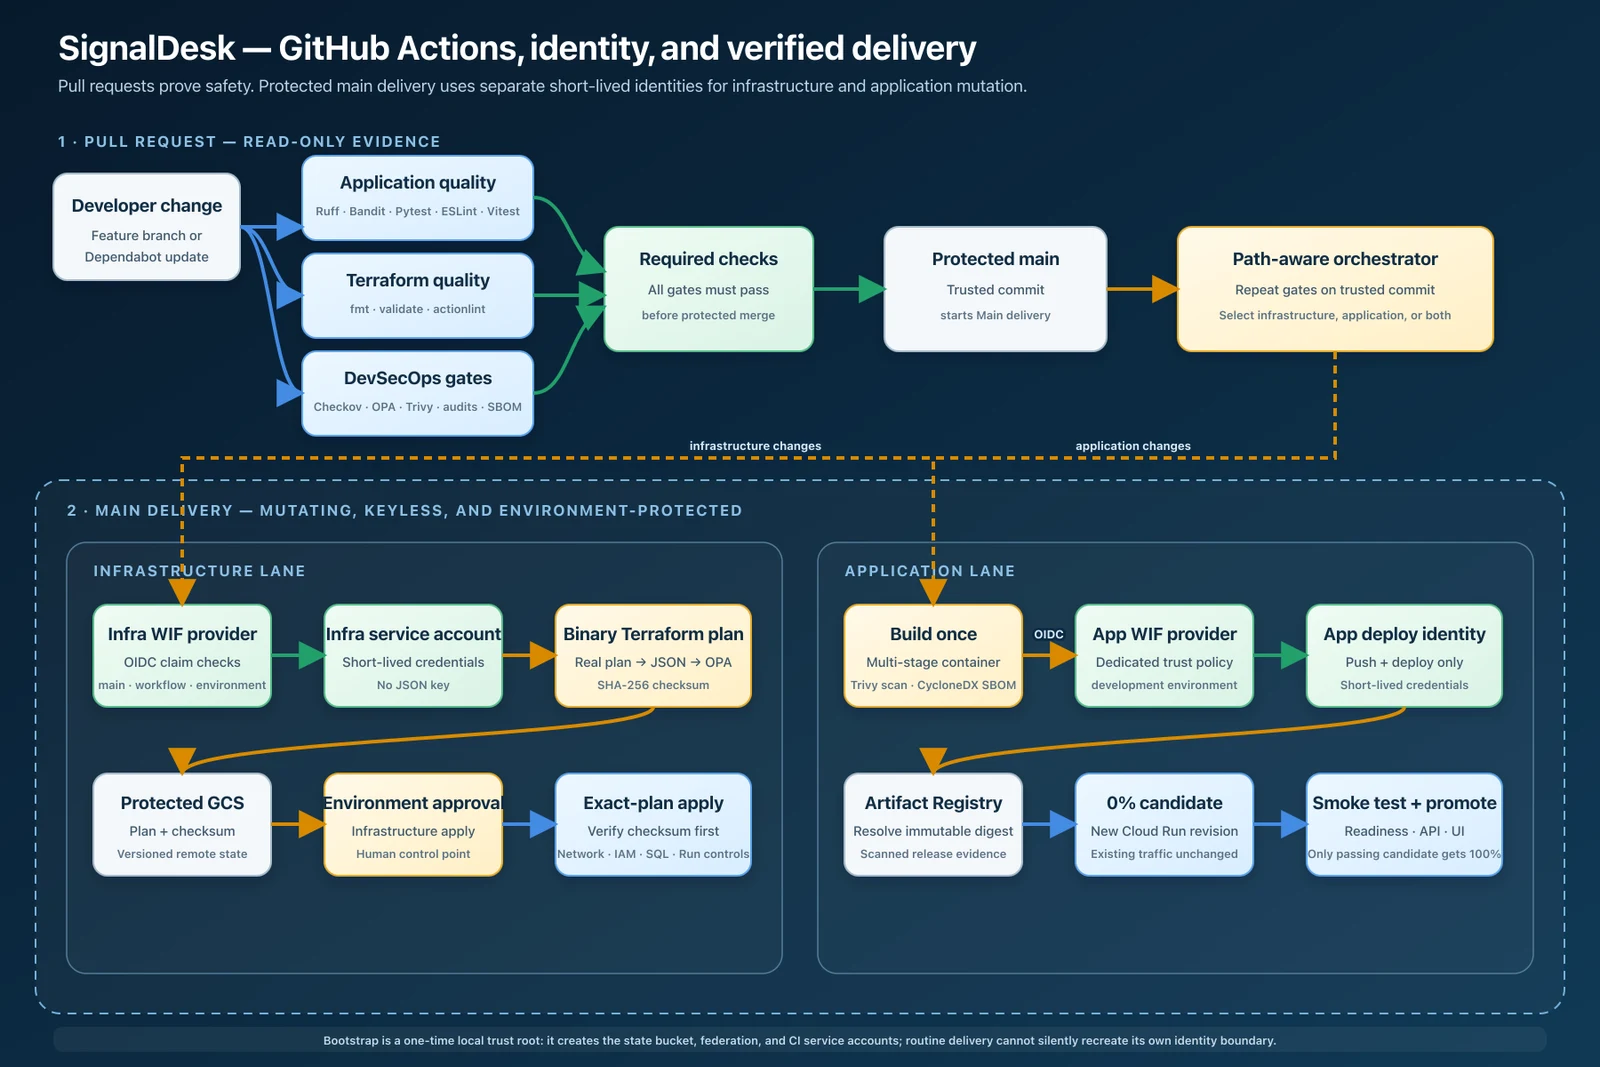
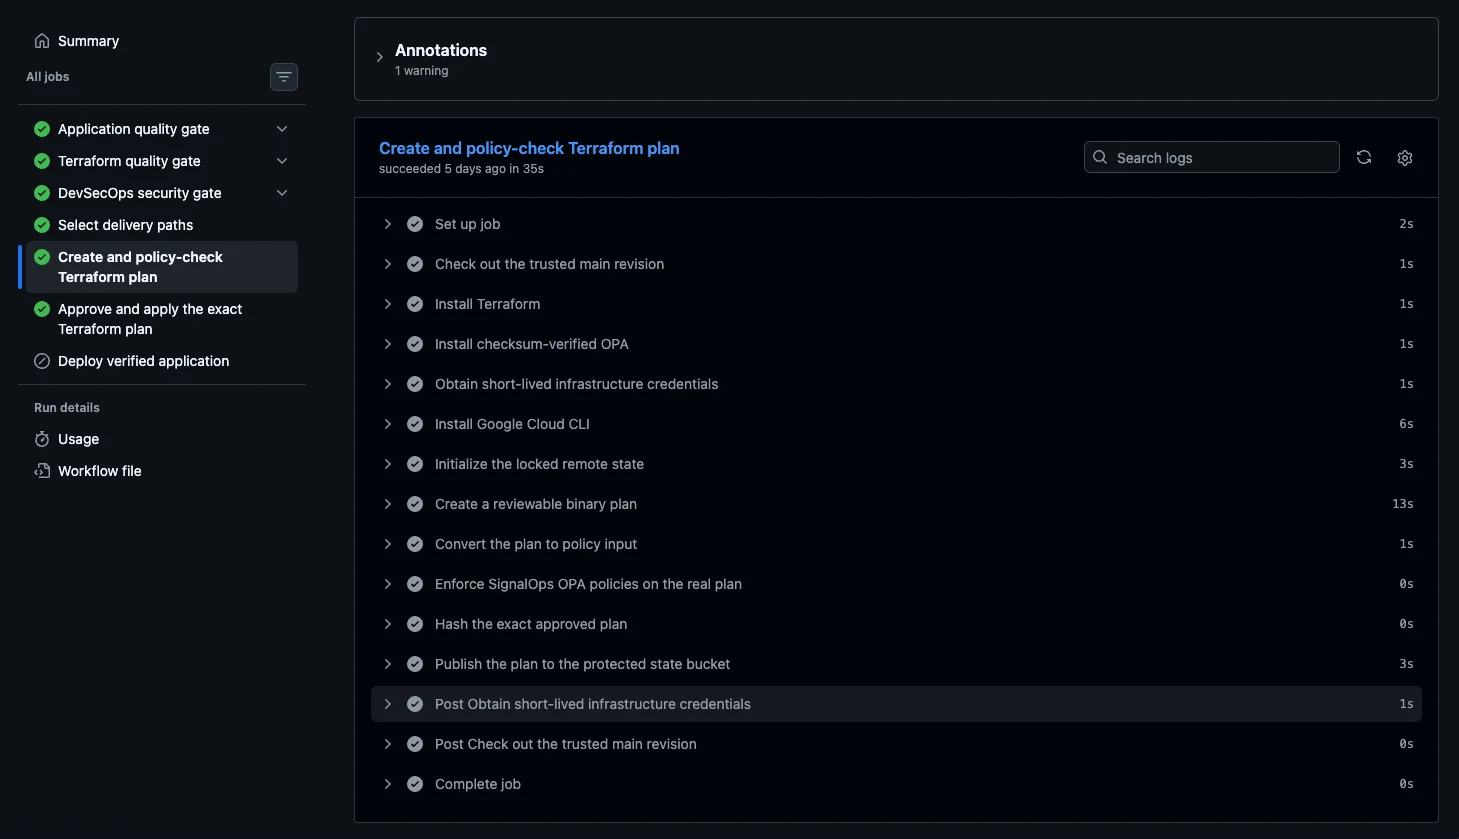
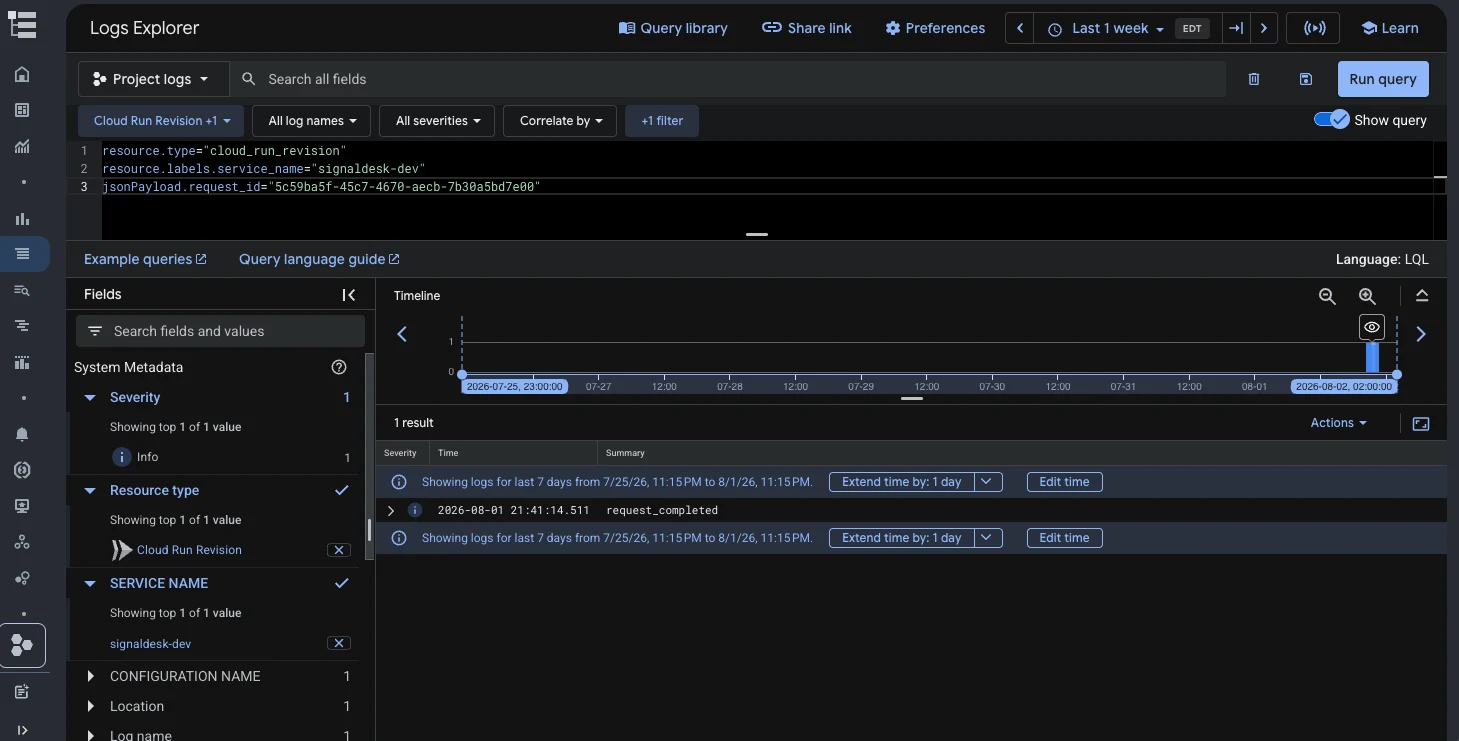
SignalDesk demonstrates a private Cloud Run and Cloud SQL data path, policy-checked Terraform delivery, keyless GitHub authentication, request-level observability, and budget alerts.
Technical practice
I focus on the systems and controls that make cloud environments understandable, repeatable, and supportable.
GCP architecture, IAM, private networking, managed runtimes, and cost-aware platform decisions.
Terraform modules, policy checks, keyless CI/CD, and repeatable environment promotion.
Service health, observability, incident signals, SLO thinking, and operational readiness.
Least-privilege identities, private data paths, secrets management, and delivery controls.
Where I add value
I translate workload requirements into infrastructure decisions, then validate those decisions through automation, security controls, and operational evidence.
Explore Google Cloud support for startups and small teamsA practical cloud foundation that supports product delivery without premature platform complexity.
Infrastructure automation and operational visibility that reduce manual work and production uncertainty.
Clearer ownership, safer delivery, and reliability practices that scale with the workload and team.
Engineering development
Graduate study strengthens how I approach software design, testing, systems architecture, and the long-term maintainability of cloud platforms.
Available for cloud engineering opportunities